White paper
The Comprehensive ISO 27001 Handbook
Download Guide Now
Fill out the form below to access the white paper.

What is ISO 27001, and why it's important?
ISO 27001 is the internationally recognized standard for establishing, implementing, maintaining, and continuously improving an Information Security Management System (ISMS). It provides a risk-based framework that helps organizations protect their information assets, digital, physical, and human, against evolving cyber threats. Published by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC), ISO 27001 defines a structured and repeatable approach to cybersecurity management, risk assessment, and security governance.
This whitepaper will explore:
- Core Principles of ISO 27001: Understanding ISMS requirements and information security objectives
- Cyber Risk Assessment and Treatment: Identifying threats, vulnerabilities, and mitigation strategies
- Annex A Security Controls: Implementing technical, organizational, and operational controls
- Security Across the SDLC: Embedding security into development, deployment, and operations
- Traceability and Compliance Documentation: Linking risks, controls, requirements, and evidence
- Digital Tools and Automation: Streamlining ISMS management, audits, and continuous compliance
1,000+ Highly Regulated Organizations Trust Visure

#1 CYBERSECURITY SOFTWARE & ALM TOOL
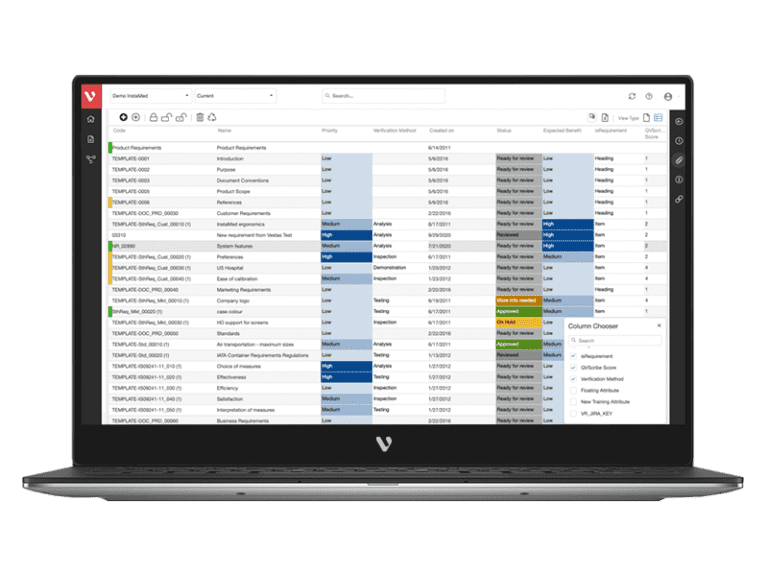
Ensure DevSecOps Compliance. Enforce Full Traceability. Accelerate Your Timelines.
See how using Visure’s Generative AI Accelerates Cybersecurity and DevSecOps throughout the product lifecycle.
- Most cost-effective
- Access All Features
- 14-day Trial
On average, our customers experience:
See what’s possible with a modern Cybersecurity ALM Software Solution for DevSecOps.
WITHIN 1ST YEAR
PER PROJECT